Close the External TLS & Domain Blind Spot in Your MSP Stack
RMM agents monitor endpoints inside the firewall—not client domain registrars, remote access VPN ports, or external web certificates. Monitor client-facing TLS and RDAP expiry externally with SLA advance alerts, PSA webhook routing, and timestamped check history.
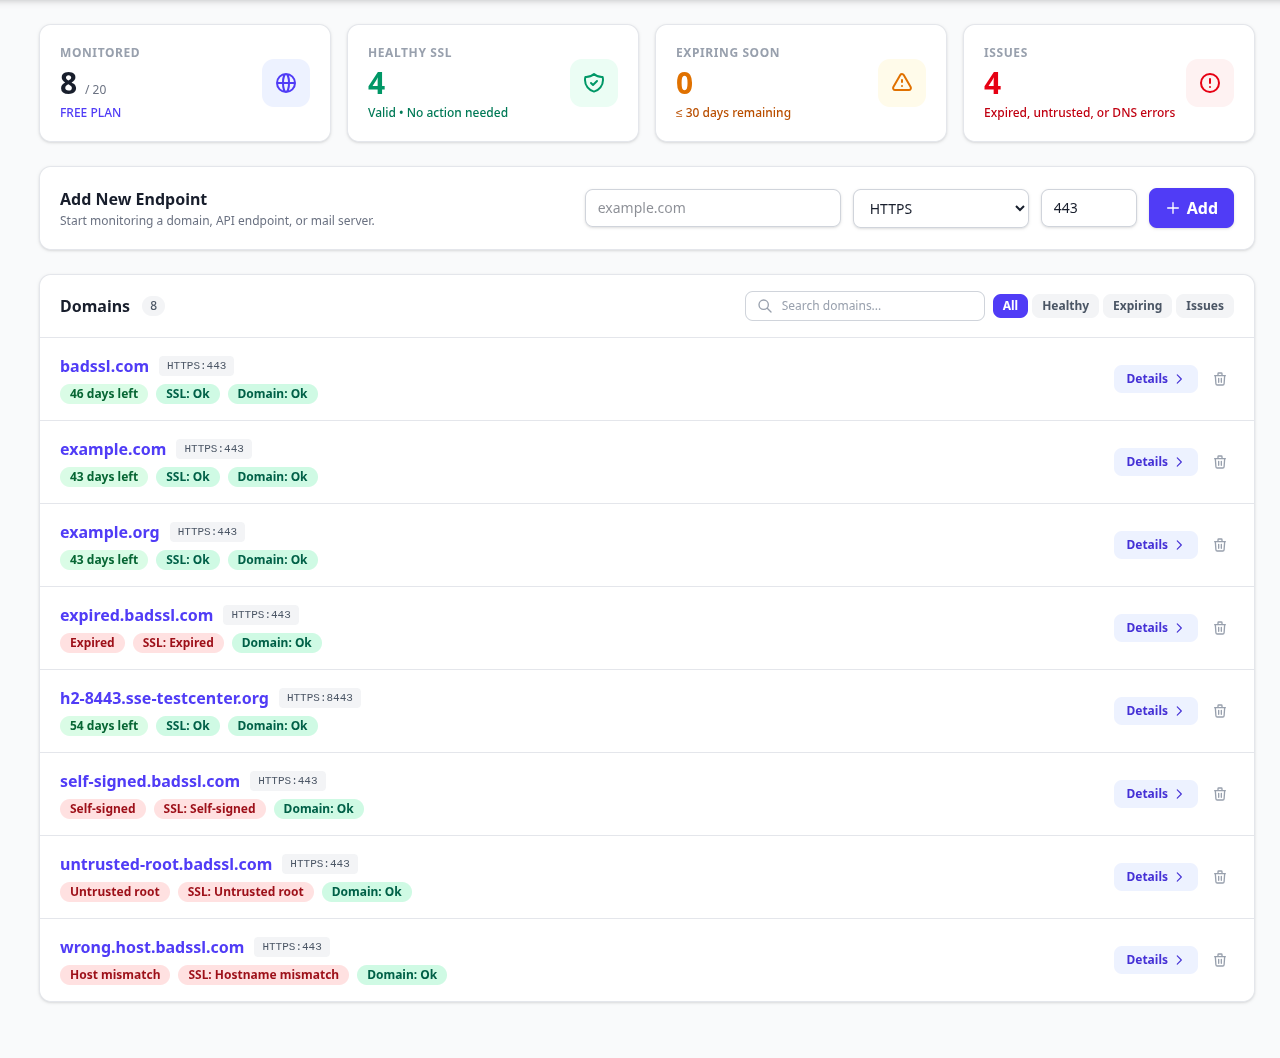
Issues or Expiring endpoints across HTTPS and custom gateway ports (:8443).
What Internal RMM Agents Miss on Client Infrastructure
Internal Windows/Linux agents can report 100% healthy while clients lose mail flow, customer portals, or remote VPN access due to external certificate or registrar expirations.
VPN, Firewall & SaaS Gateways
SSL VPN portals, RDWeb gateways, and appliances often cannot run RMM scripts. Monitor them externally on :443 or custom ports like :8443 / :10443 alongside mail (:465, :993) and LDAPS :636.
Shadow Registrar & DNS Failures
Client accounting teams cancel a corporate card tied to an old registrar account—taking down Microsoft 365 / Google Workspace MX routing overnight. Adaptive RDAP & WHOIS tracking warns MSPs well before redemption or dns.nxdomain occurs.
Hardened Operator Access
Lock down your MSP monitoring console with phishing-resistant Passkeys / WebAuthn (YubiKey, Windows Hello, Touch ID) plus TOTP two-factor authentication.
Verifiable Check History & Staged SLA Lead Times
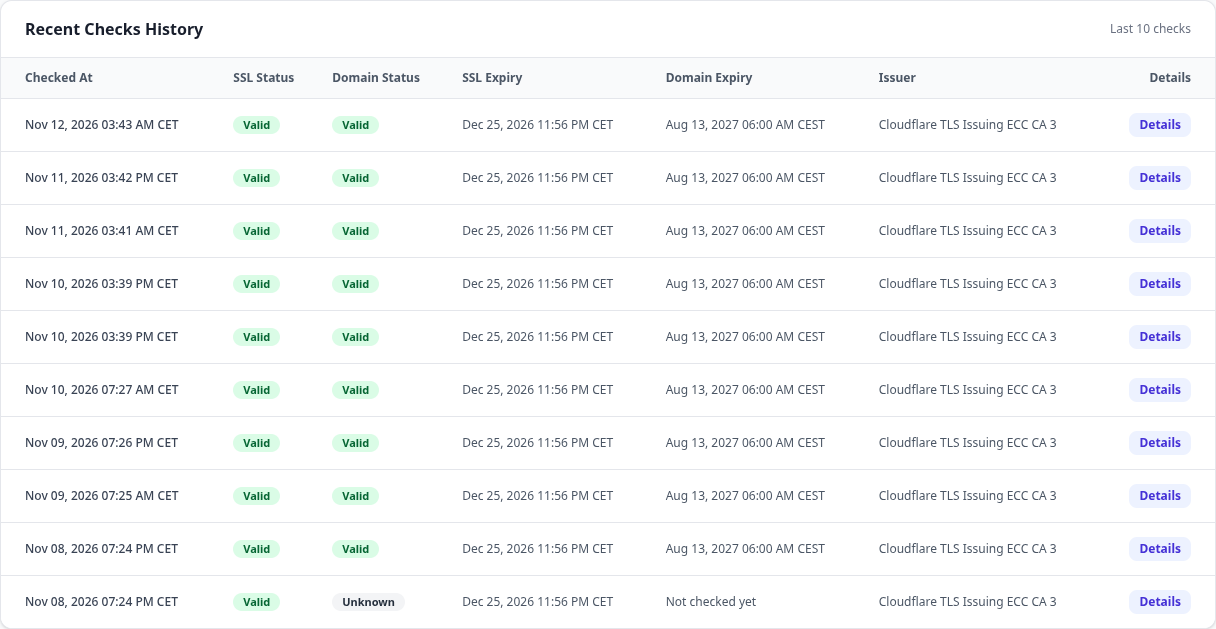
Every monitored endpoint maintains a chronological check history showing SSL status, domain status, expiration dates, issuing CA, and scan timestamps (every 12h by default, or 24h / weekly).
- Configurable Advance Window: Choose 30, 21, 14, 10, 7, 5, 3, or 2 days notice to fit client CAB schedules.
- Mandatory 1-Day Final Alert: High-urgency escalation triggers automatically at 24h remaining.
- Daily Renewal Digest: Optional summary email tracking rotated serial numbers when auto-renewals complete.
Route Renewal Tickets Straight Into Your Service Desk
Point ExpiryHawk webhooks at your PSA middleware (n8n, Make, Power Automate, Azure Functions, or internal NOC API) to open actionable renewal tickets before users are impacted.
ssl.expiring / domain.expiring)Create a P3 maintenance ticket containing exact data.target, data.days_left, and direct links.domain_url.
ssl.renewed)Detect rotated certificate serial numbers cleanly and append confirmation notes or close completed maintenance tickets automatically.
Pair webhook ticket creation (with automatic 5xx retries at +1m, +5m, +15m) with Email distribution lists, Telegram, Browser Push, or WhatsApp via BeepMate.
{
  "id": "wh_24c09a1e7d11",
  "event": "domain.expiring",
  "created_at": 1794320400,
  "timestamp": "2026-11-10T15:00:00Z",
  "data": {
    "target": "portal.clientcorp.com:443",
    "domain": "portal.clientcorp.com",
    "protocol": "https",
    "port": 443,
    "monitor_type": "domain",
    "status": "expiring",
    "milestone": "14d",
    "days_left": 14,
    "expiry_date": "2026-11-24T00:00:00Z",
    "message": "Domain registration expires in 14 days.",
    "links": {
      "domain_url": "https://expiryhawk.com/domain/108",
      "dashboard_url": "https://expiryhawk.com/dashboard"
    }
  }
}
Frequently Asked Questions for MSPs
Why do MSPs need external SSL and domain monitoring if they already run an RMM?
RMM agents watch workloads inside client environments—not client domain registrars, external DNS resolution, perimeter VPN SSL listeners, or CDN certificates. ExpiryHawk monitors client domains externally and checks ICANN RDAP and WHOIS expiration status for supported TLDs.
Can ExpiryHawk trigger tickets in our PSA or automation workflow via webhooks?
Yes. Configure HTTP POST or PUT webhooks with custom authentication headers, HMAC-SHA256 signatures, and subscribed events (ssl.expiring, ssl.expired, domain.expiring, dns.nxdomain, ssl.renewed).
How can we align alert timing with our MSP change-management windows?
Select an advance notice threshold of 30, 21, 14, 10, 7, 5, 3, or 2 days so renewals enter client maintenance queues smoothly, backed by a mandatory 1-day final urgent reminder.
How is our monitoring account protected against credential attacks?
Operator accounts support phishing-resistant FIDO2 Passkeys and hardware security tokens (YubiKey, Windows Hello, Touch ID) alongside TOTP two-factor authentication.
Explore Other Solutions
Bring external TLS and domain visibility into your MSP toolkit
Validate the workflow with 20 free endpoints—or expand up to 500 endpoints as your client coverage grows.