External SSL & TLS Monitoring Built for Web Developers
Catch silent ACME and Certbot renewal failures, incomplete intermediate CA chains, weak cipher suites, and forgotten staging ports from outside your network—before API clients, curl scripts, or browsers fail TLS handshakes.
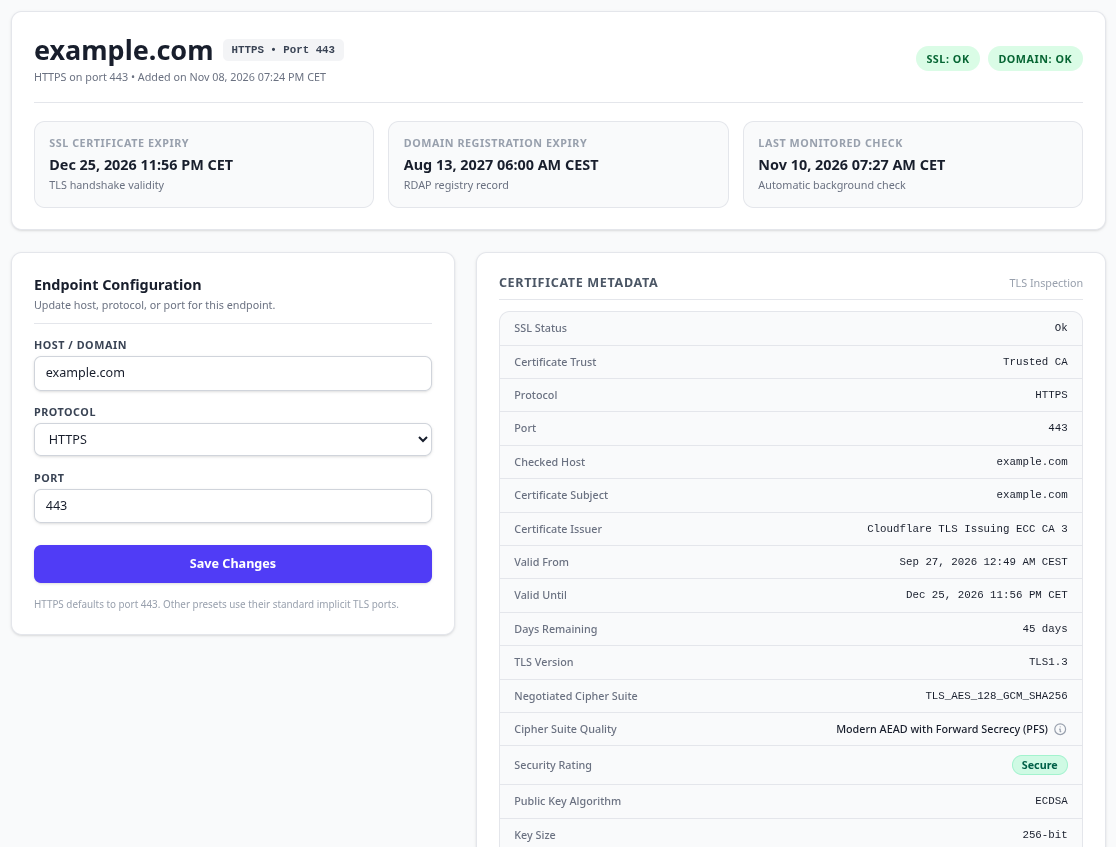
Real TLS Failure Modes Developers Hit in Production
Local renewal cron jobs only confirm whether a file changed on disk. Monitoring externally every 12 hours, 24 hours, or weekly verifies what users and downstream services actually negotiate over TLS.
Silent ACME & Reload Failures
A firewall rule blocks HTTP-01 challenges, a Cloudflare DNS token expires, or Certbot renews cleanly on disk without reloading Nginx or HAProxy. ExpiryHawk flags non-renewing certificates ahead of deadline via your chosen threshold (30 to 2 days) plus a mandatory 1-day urgent alert.
Read: Monitoring ACME auto-renewals →“Works in Chrome, Fails in cURL”
Desktop browsers often fill in missing intermediate certificates using cached certs or AIA chasing. REST clients, mobile apps, and backend workers reject incomplete chains immediately. We surface full CA Chain Subjects and trust status (Untrusted / Host mismatch).
Forgotten Staging & API Ports
Production :443 gets automated while a staging webhook listener on :8443 or internal gateway expires quietly. Add the same hostname on multiple ports—each (host, port) pair is tracked independently.
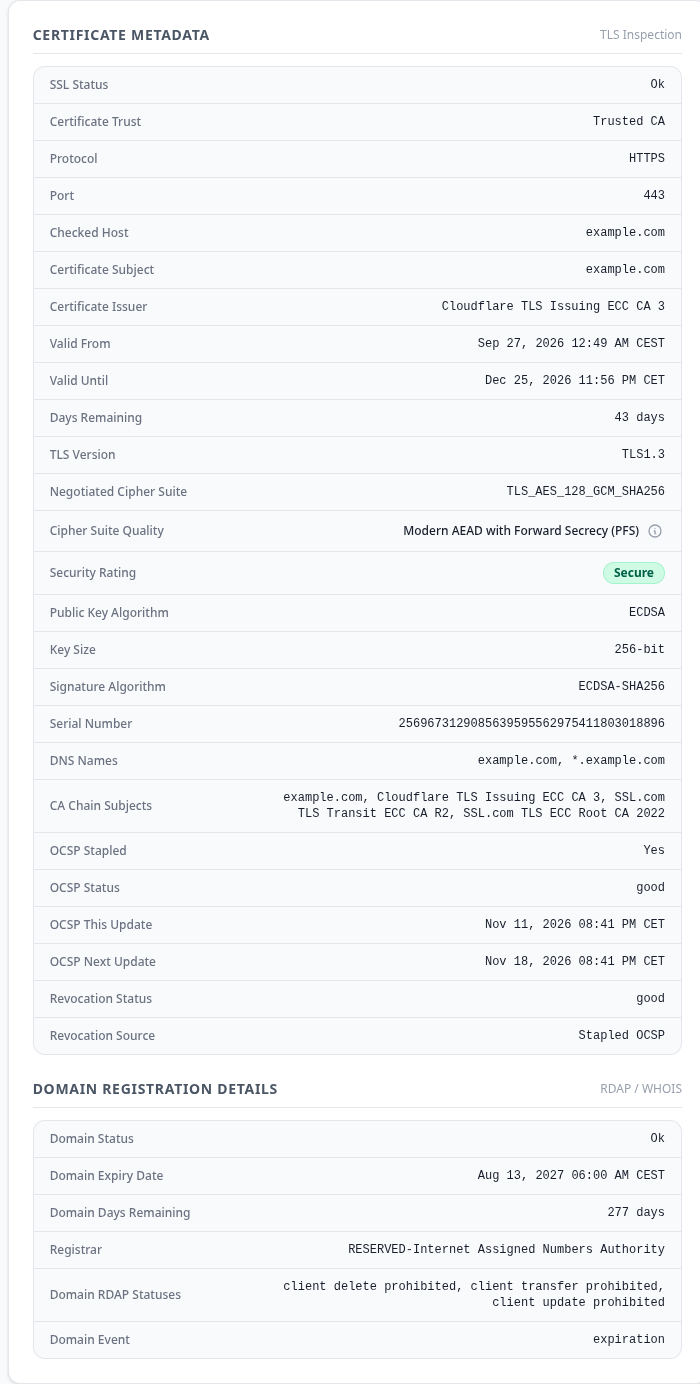
Audit SAN Lists, CA Chains, OCSP Stapling & Domain Locks
Inspect full X.509 handshake outputs without dropping to openssl s_client every deploy:
- DNS Names (SANs): Confirm every apex and wildcard hostname matches what your load balancer expects.
-
Cipher Quality & PFS: Classify negotiated suites (e.g.,
TLS_AES_128_GCM_SHA256) against our cipher suite quality guide. -
OCSP Stapling & Chain Audit: Verify
OCSP Stapled: Yes, OCSP response status, andCA Chain Subjects. -
RDAP & WHOIS Registration Tracking: Monitor registrar expiry and EPP locks (
clientTransferProhibited) for supported TLDs.
HMAC-Signed Webhooks Built for Your Pipelines
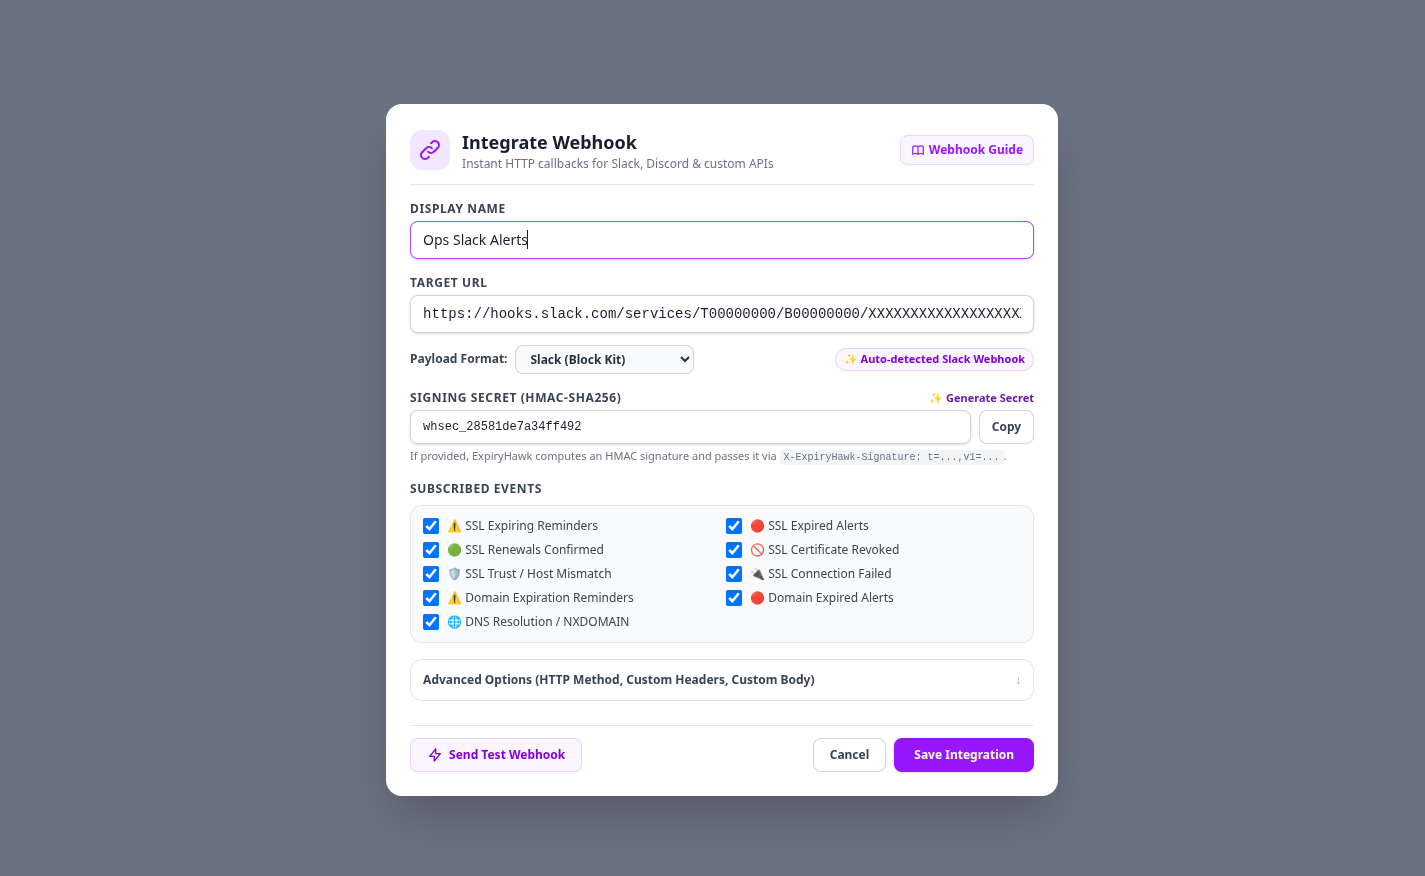
Route expiry, trust, NXDOMAIN, and renewal events straight into ChatOps, PagerDuty bridges, or custom bots alongside Telegram, Email, Browser Push, and WhatsApp alerts.
-
•
Slack & Discord auto-detection: Paste a
hooks.slack.comor Discord webhook URL for native Block Kit / Rich Embed formatting. -
•
Event filtering: Subscribe selectively to
ssl.expiring,ssl.expired,ssl.renewed,domain.expiring,dns.nxdomain, orping.test. -
•
Custom headers & HMAC-SHA256: Send
POSTorPUTrequests withX-ExpiryHawk-Signatureverification, SSRF filtering, 10s timeouts, and 5xx retries (+1m, +5m, +15m).
{
  "id": "wh_8f31c2a9b40e",
  "event": "ssl.expiring",
  "created_at": 1794318000,
  "timestamp": "2026-11-10T14:20:00Z",
  "data": {
    "target": "api.staging.example.com:8443",
    "domain": "api.staging.example.com",
    "protocol": "https",
    "port": 8443,
    "monitor_type": "ssl",
    "status": "expiring",
    "milestone": "7d",
    "days_left": 7,
    "expiry_date": "2026-11-17T14:20:00Z",
    "issuer": "Let's Encrypt",
    "subject": "api.staging.example.com",
    "message": "SSL certificate expires in 7 days.",
    "certificate": {
      "serial_number": "04:9A:...:3F",
      "valid_to": "2026-11-17T14:20:00Z"
    },
    "links": {
      "domain_url": "https://expiryhawk.com/domain/42",
      "dashboard_url": "https://expiryhawk.com/dashboard"
    }
  }
}const parts = Object.fromEntries(sigHeader.split(',').map(p => p.split('=')));
const expected = crypto.createHmac('sha256', SECRET)
.update(`${parts.t}.${rawBody}`).digest('hex');
const valid = crypto.timingSafeEqual(Buffer.from(expected), Buffer.from(parts.v1));Inspect Any TLS Endpoint Right Now
Run an on-demand external certificate, CA chain, and cipher check via our free public tool before creating an account.
Frequently Asked Questions for Developers
Why monitor SSL externally if Certbot or Prometheus runs on my server?
On-box checks read files on disk or probe localhost. They miss reverse proxies holding an old cert before reload, load balancers with stale secrets, CDN origin misconfigurations, and public DNS errors. ExpiryHawk connects over the public internet twice daily so you see what external callers negotiate.
How do I verify ExpiryHawk webhook signatures in my application?
When a webhook secret is configured, ExpiryHawk sends an X-ExpiryHawk-Signature header formatted as t=<unix_timestamp>,v1=<hmac_sha256_hex>. Hash <timestamp>.<raw_body> with HMAC-SHA256 using your secret and compare digests safely.
Can I monitor the same hostname on both port 443 and a custom port like 8443?
Yes. Endpoints are unique by host and port together, allowing you to watch production HTTPS on port 443 alongside staging APIs or custom reverse proxy listeners on any TCP port from 1 to 65535.
Which TLS metadata and certificate checks are included?
Each check inspects TLS version, negotiated cipher suite and Forward Secrecy rating, key algorithm and bit size, SAN DNS entries, full intermediate CA chain, OCSP stapling status and update window, plus IANA RDAP and port 43 WHOIS domain registration expiry.
Explore Other Solutions
Start external SSL & domain monitoring in under a minute
Monitor up to 20 endpoints free with external TLS inspection, RDAP expiry tracking, and signed webhooks.